A bar volunteer who accidentally issues a refund. An intern exporting the full attendee list. As long as everyone with dashboard access can do everything, every team member is a risk — not out of malice, but because one wrong click is enough. That's why the MijnEvent dashboard now works with permissions per team member: you decide who sees what, and who may do what.
Five templates to start from
When you invite a new team member you pick a permission template right away: Full management, Events, Finance, Marketing & content or Read-only. If you pick nothing, the new member starts with Read-only — looking around is fine, touching anything is not.
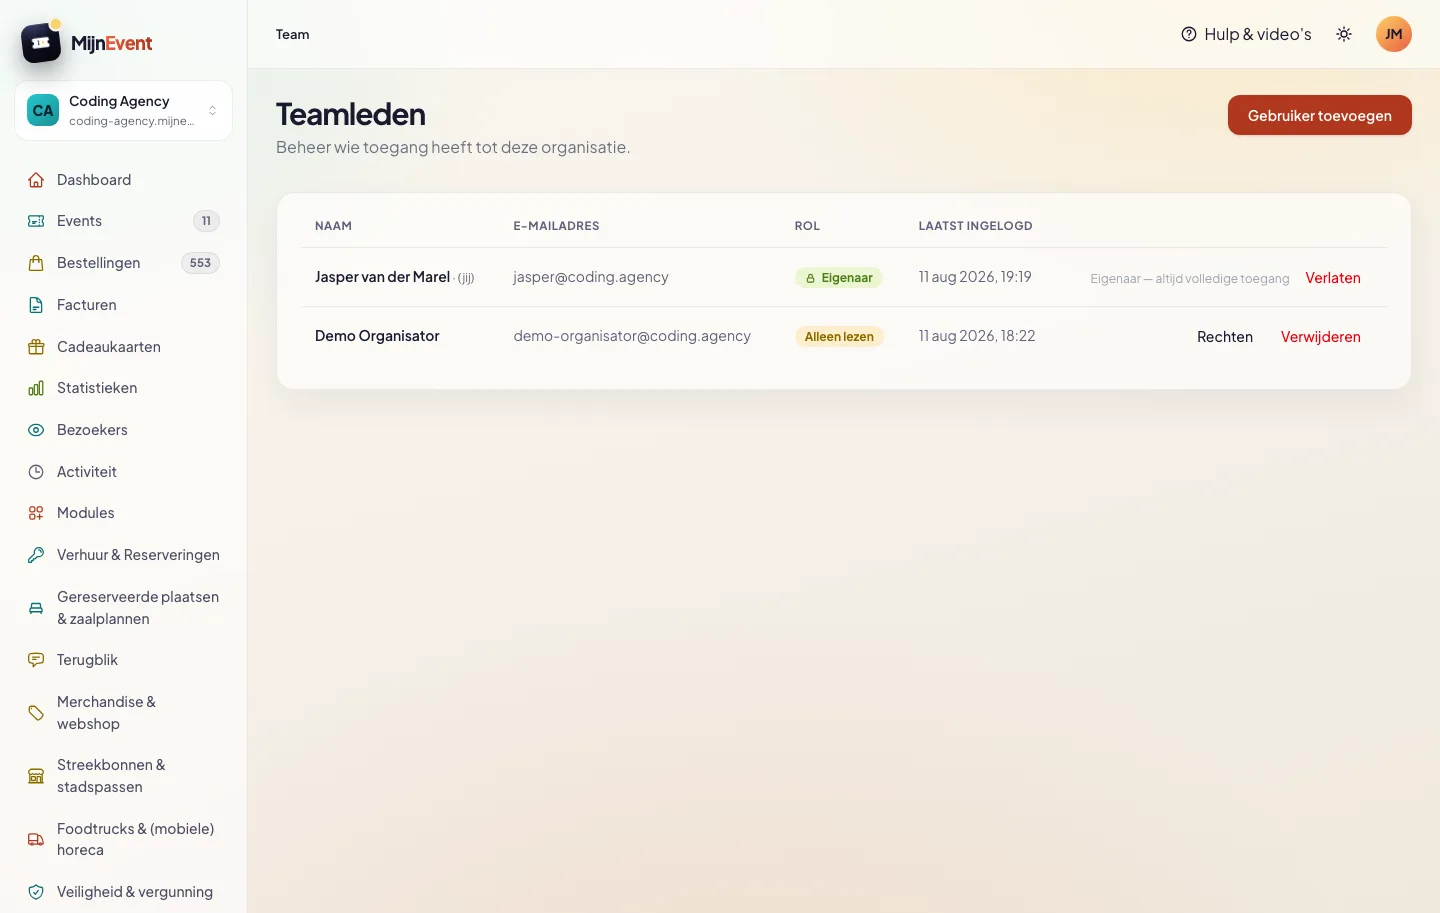
A template is a starting point, not a straitjacket. After inviting you adjust everything per user; the label in the team list then changes to "Custom", so you can tell at a glance who has a standard profile and who has tailored access.
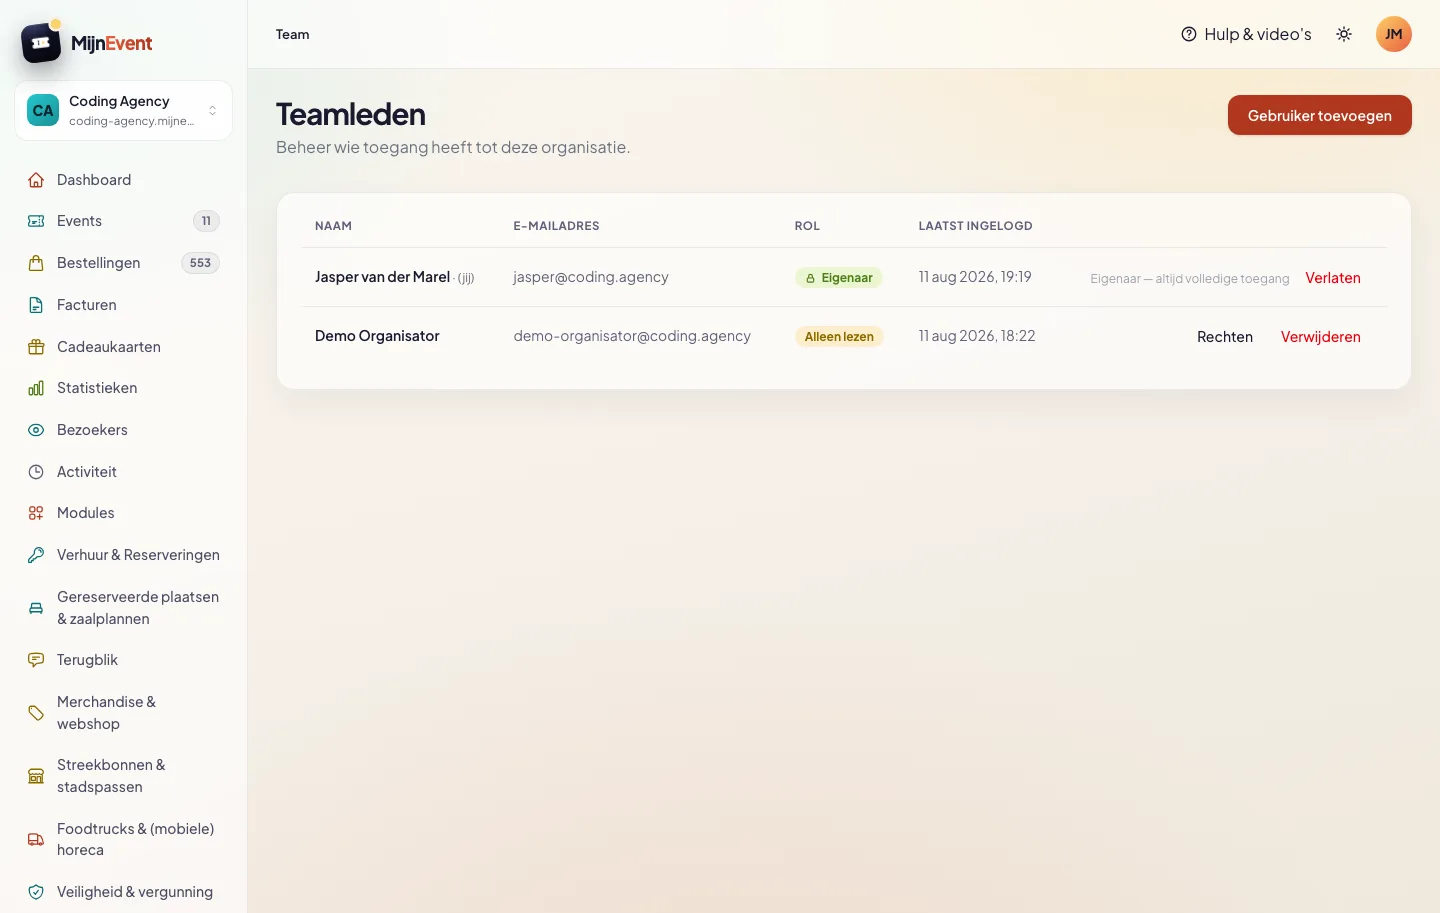
The matrix: None, View or Manage
Click Permissions next to a team member and the permissions panel slides open. Every section of the dashboard — events, orders, invoices, gift cards, statistics, team, GDPR requests, settings, branding and the activity log — has three levels: None (invisible), View (read, change nothing) or Manage (everything).
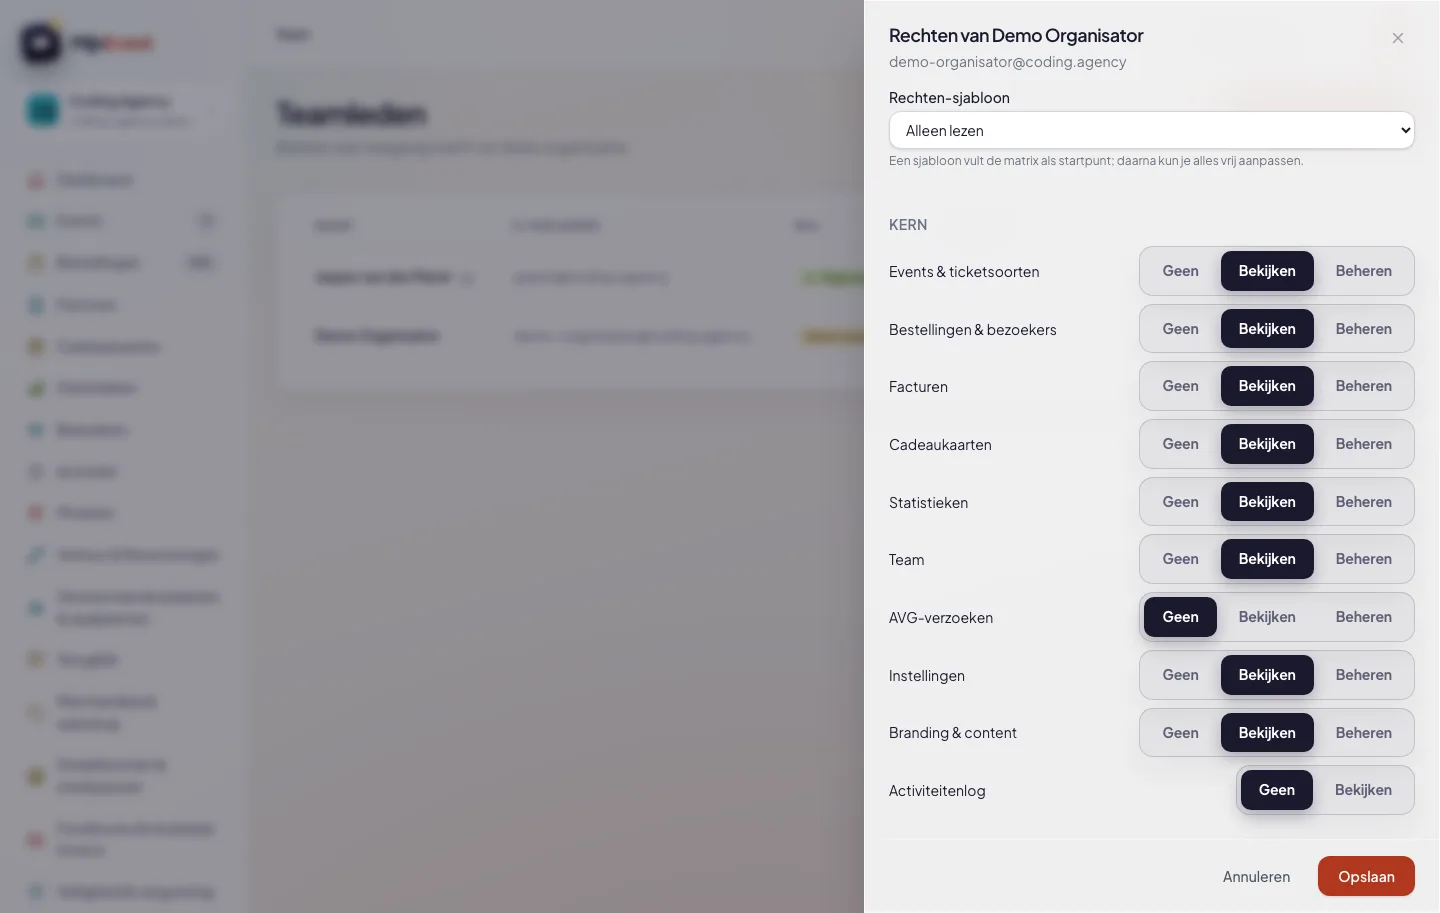
Below the core sections you'll find your active modules, with exactly the same three levels. A module that is enabled for your organisation is no longer automatically open to the whole team.
Sensitive actions are enabled deliberately
Some actions deserve their own threshold, even for team members who can otherwise do a lot: issuing refunds, erasing or exporting personal data (GDPR), publishing events (which starts a payment), managing the Mollie connection and switching pricing plans. These live as separate switches in a highlighted block — and a switch only becomes available once the related section is at least set to View.
The same principle applies inside modules. Being able to see the city-card administration does not mean you can run a payout round or download the SEPA file for the bank: that is its own sub-permission. Sending mass mailings, starting an evacuation, paying out food-truck settlements and settling deposits are separate sub-permissions too.
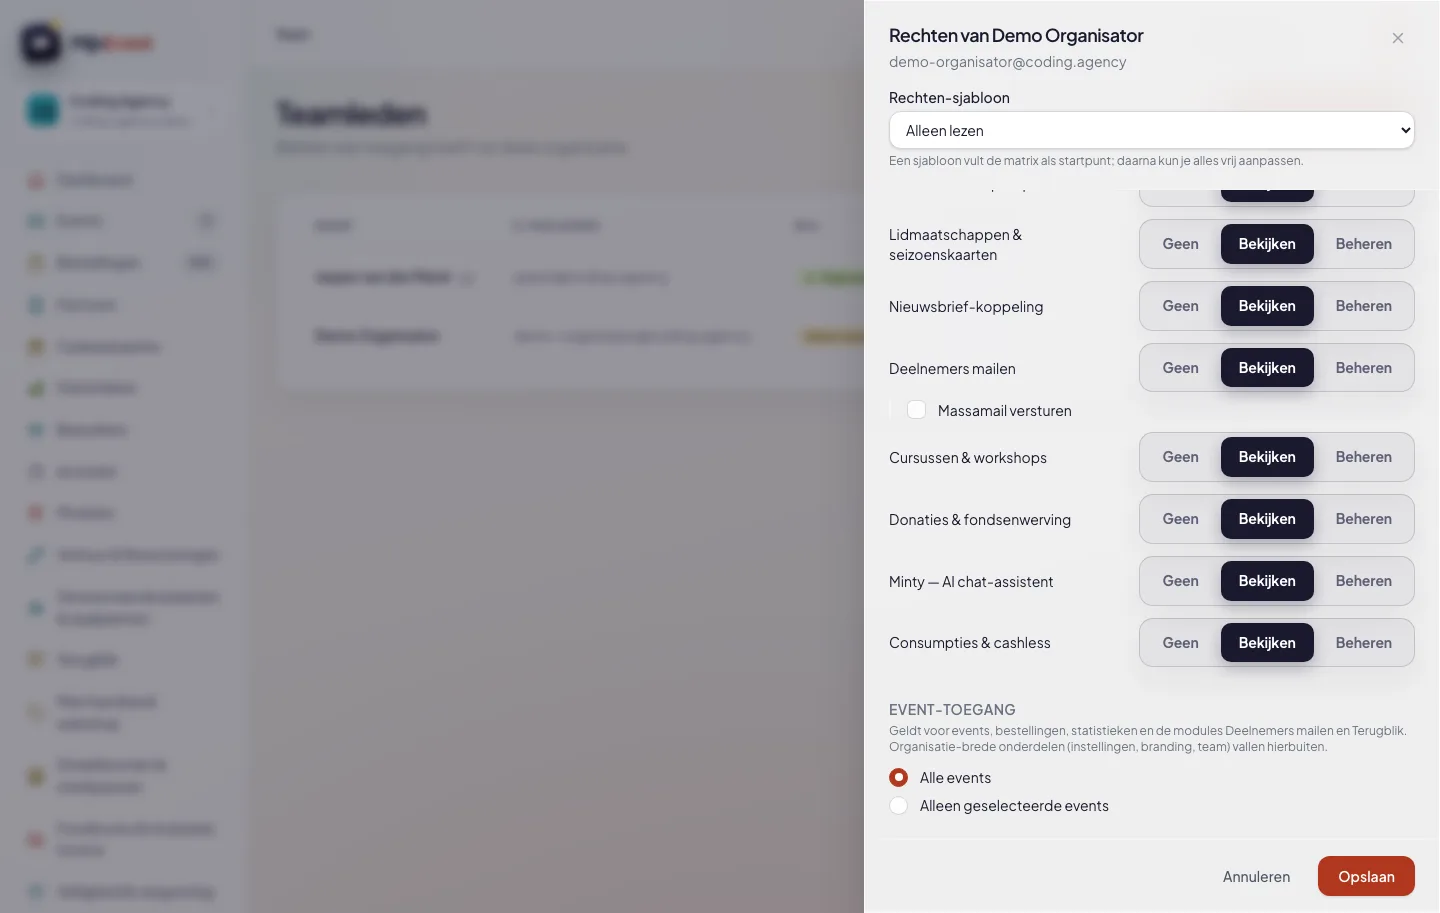
Access to a single event
Working with a production lead per festival or a treasurer per edition? Then limit event access: instead of "all events" you select the events this team member may work on. Lists, orders, statistics, exports, attendee mailings and Terugblik then only show those events — even the revenue figures on the dashboard only count their own events. Organisation-wide sections such as settings and branding sit outside that restriction; you control those with the matrix.
No permission? Then it's not there
The navigation only shows what a team member has permission for. Anyone who opens a direct link anyway — or just lost a permission — gets a clear message and lands on the first page that is allowed:
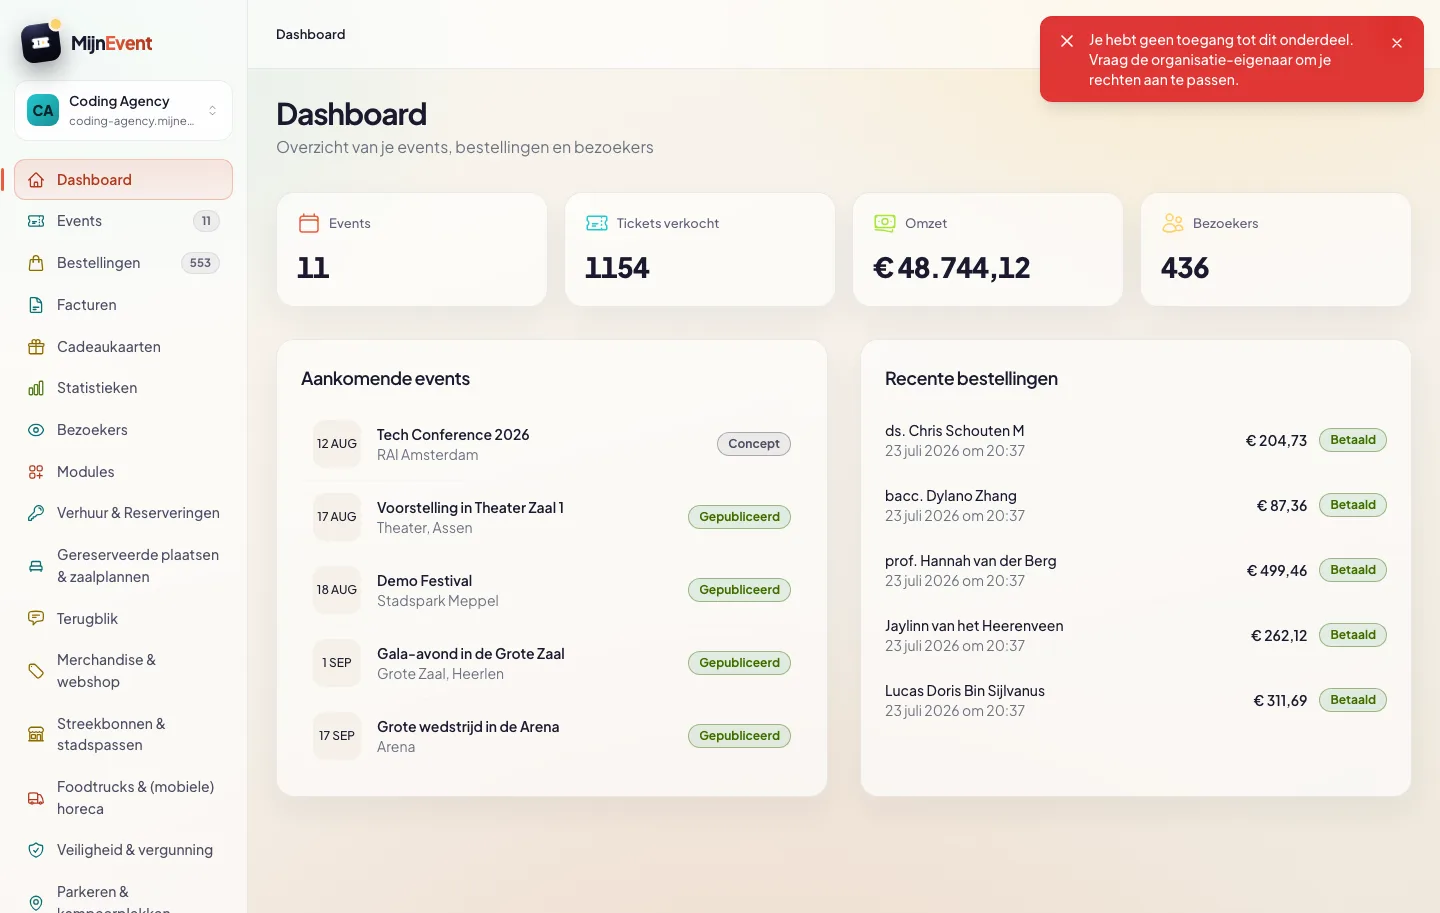
More important than what the screen shows: the server checks every request itself. Even someone who bypasses the screens and calls the API directly gets no further than their permissions.
Extra locks on the most dangerous actions
Three actions ask for more than a permission alone. Downloading a SEPA payment file, permanently erasing personal data and disconnecting Mollie require a fresh two-factor code — right before the action, even when you are already logged in. And city-card payout rounds follow the four-eyes principle: whoever creates the round cannot mark it as sent themselves; a second team member with payout permissions does that.
Every permission change is also written to the activity log, including exactly what changed. That log used to be owner-only; it is now an assignable permission as well — though deliberately part of no template, so the owner always grants it explicitly.
This way your team grows without handing out access you'd rather keep to yourself. Start broad or start narrow — adjusting is always two clicks.